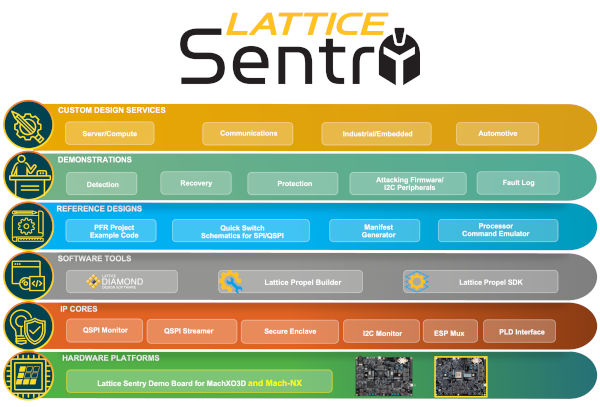
The solution stack enables next-generation Root-of-Trust (HRoT) hardware solutions that comply with NIST Platform Firmware Resiliency (PFR) guidelines (NIST SP-800-193) and support 384-bit encryption. This new version of Lattice Sentry addresses the rapidly evolving security requirements of current and emerging server platforms, providing developers with an efficient and secure way to quickly deploy enhanced cryptographic and system applications. The stack supports firmware security for the communications, computing, industrial, automotive, and smart consumer markets.
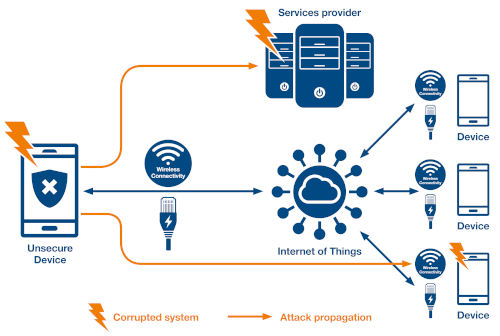
The Cloud Security Industry Summit is a group of cloud service providers working to align the industry with best-in-class security solutions. In an article co-authored with the Open Compute Project (OCP), the CSIS states that "firmware represents a significant threat vector for computing systems, appliances, and associated infrastructure. If the first code that runs on a device when it is powered on is compromised, the entire system can and should become insecure. Firmware can be compromised through malicious or unintentional attacks.".
“Keeping abreast of evolving cybersecurity threats is a constant struggle for most organizations. To help them keep pace, Lattice is committed to continuously improving the security, performance, and usability capabilities of our Sentry Stack,” said Eric Sivertson, vice president of the security business at Lattice Semiconductor. “Lattice has long been a leader in server control solutions, and Lattice Control PLDs are the first power-on/power-off component in many servers currently in service. With the Sentry Stack, developers can easily add support for strong firmware security to system control applications based on Lattice Secure Control PLDs, creating an ideal platform for establishing a High-Resolution Operation (HRoT) that validates the legitimacy of all firmware instances in a system.”
The main features of Sentry 2.0 include
- Enhanced Security - The Sentry solution stack supports the Lattice Mach™-NX secure control FPGA and a secure enclave IP block that enables 384-bit cryptography (ECC-256/384 and HMAC-SHA-384) to better secure Sentry-protected firmware against unauthorized access. Support for 384-bit cryptography is a requirement for many next-generation server platforms.
- 4x Faster Pre-Boot Authentication - Sentry 2.0 supports faster ECDSA (40 ms), SHA (up to 70 Mbps), and QSPI (64 MHz) throughput. These features enable Sentry 2.0 to deliver faster boot times, helping to minimize system downtime and reduce exposure to firmware attack attempts during the boot process.
- Ability to monitor up to five firmware images in real time - To further expand the PFR-compatible HRoT enabled by Lattice Sentry, the stack is capable of real-time monitoring of up to five motherboard components in a system during boot and operation. Competing MCU-based security solutions, for example, lack the processing power required to adequately monitor so many components in real time.