




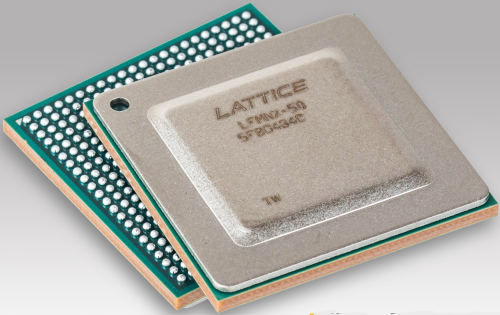
as well as in computer, communications, industrial, and automotive systems. Mach-NX marks the third FPGA family developed in one year on the Lattice Nexus™ FPGA platform.
“The race is on between bad actors trying to exploit firmware vulnerabilities and developers designing server platforms with the security features and performance to stop them,” says Patrick Moorhead, president and founder of Moor Insights & Strategy. “Securing systems requires real-time HRoT with support for stronger cryptography algorithms like ECC 384 and robust new data security protocols like SPDM. Lattice’s Mach FPGA families can simplify and accelerate the deployment of these technologies for server OEMs looking to secure their platforms against cyberattacks and IP theft.”
Esam Elashmawi, Director of Strategy and Marketing at Lattice, states: “Securing systems against unauthorized firmware access goes beyond establishing a High-Resolution Erasure (HRoT) at boot. It also requires that the components used to build the system are not compromised as they move through the global supply chain. When combined with the additional protection offered by our SupplyGuard security service, Lattice Mach-NX FPGAs can protect a system throughout its entire lifecycle: from the moment components begin moving through the supply chain, through initial product assembly, final product shipment, integration, and throughout the product's operational life.”
Building on the system control capabilities of the Mach family, Mach-NX FPGAs combine a secure enclave (an advanced 384-bit hardware-based encryption engine that supports reprogrammable bitstream protection) with a logic cell (LC) and an I/O block. The secure enclave helps secure the firmware, and the LC and I/O block enable system control functions such as power management and fan control. Mach-NX FPGAs can verify and install over-the-air firmware updates that keep systems compliant with evolving security guidelines and protocols. The parallel processing architecture and dual-boot flash memory configuration of the Mach-NX FPGA provide the near-instantaneous response times needed to detect and recover from attacks—a level of performance that surpasses the capabilities of other HRoT platforms such as MCUs. Mach-NX FPGAs will support the Lattice Sentry™ solution stack, a robust combination of customizable embedded software, reference designs, IP, and development tools to accelerate the deployment of secure systems that meet the NIST Platform Firmware Resilience Guidelines (PFR) (NIST SP-800-193).
Key features of the Mach-NX family include:
- Secure system control - The logic of Mach-NX FPGAs (up to 11K LCs) and the high number of I/O points (up to 379) enable fast and secure system control. Lattice is a long-standing leader in programmable logic for system control. Mach FPGAs have a fix rate of over 80 percent on current shipping server platforms.
- Robust standards and protocol compliance - The 384-bit hardware encryption engine of Mach-NX FPGAs supports quick and easy implementation of cutting-edge cryptography such as ECC 384 and industry-standard security protocols such as NIST SP-800-193 and MCTP-SPDM. Future server platforms will require support for these protocols.
- End-to-end supply chain protection - Mach-NX FPGAs are backed by the Lattice SupplyGuard™ supply chain security subscription service. SupplyGuard gives OEMs and ODMs peace of mind by tracking locked Lattice FPGAs throughout their entire lifecycle, from the point of manufacture, through transportation across the global supply chain, system integration and assembly, initial configuration, and deployment.
The Lattice Propel™ design environment is rapidly customizable, accelerating the design of a custom, PFR-compliant HRoT solution. The tool utilizes a graphical user interface-based development environment that allows developers to create PFR solutions while minimizing the need to write RTL code.
To learn more about the network technologies mentioned above, please visit:








